CIS compliance, checked in seconds.
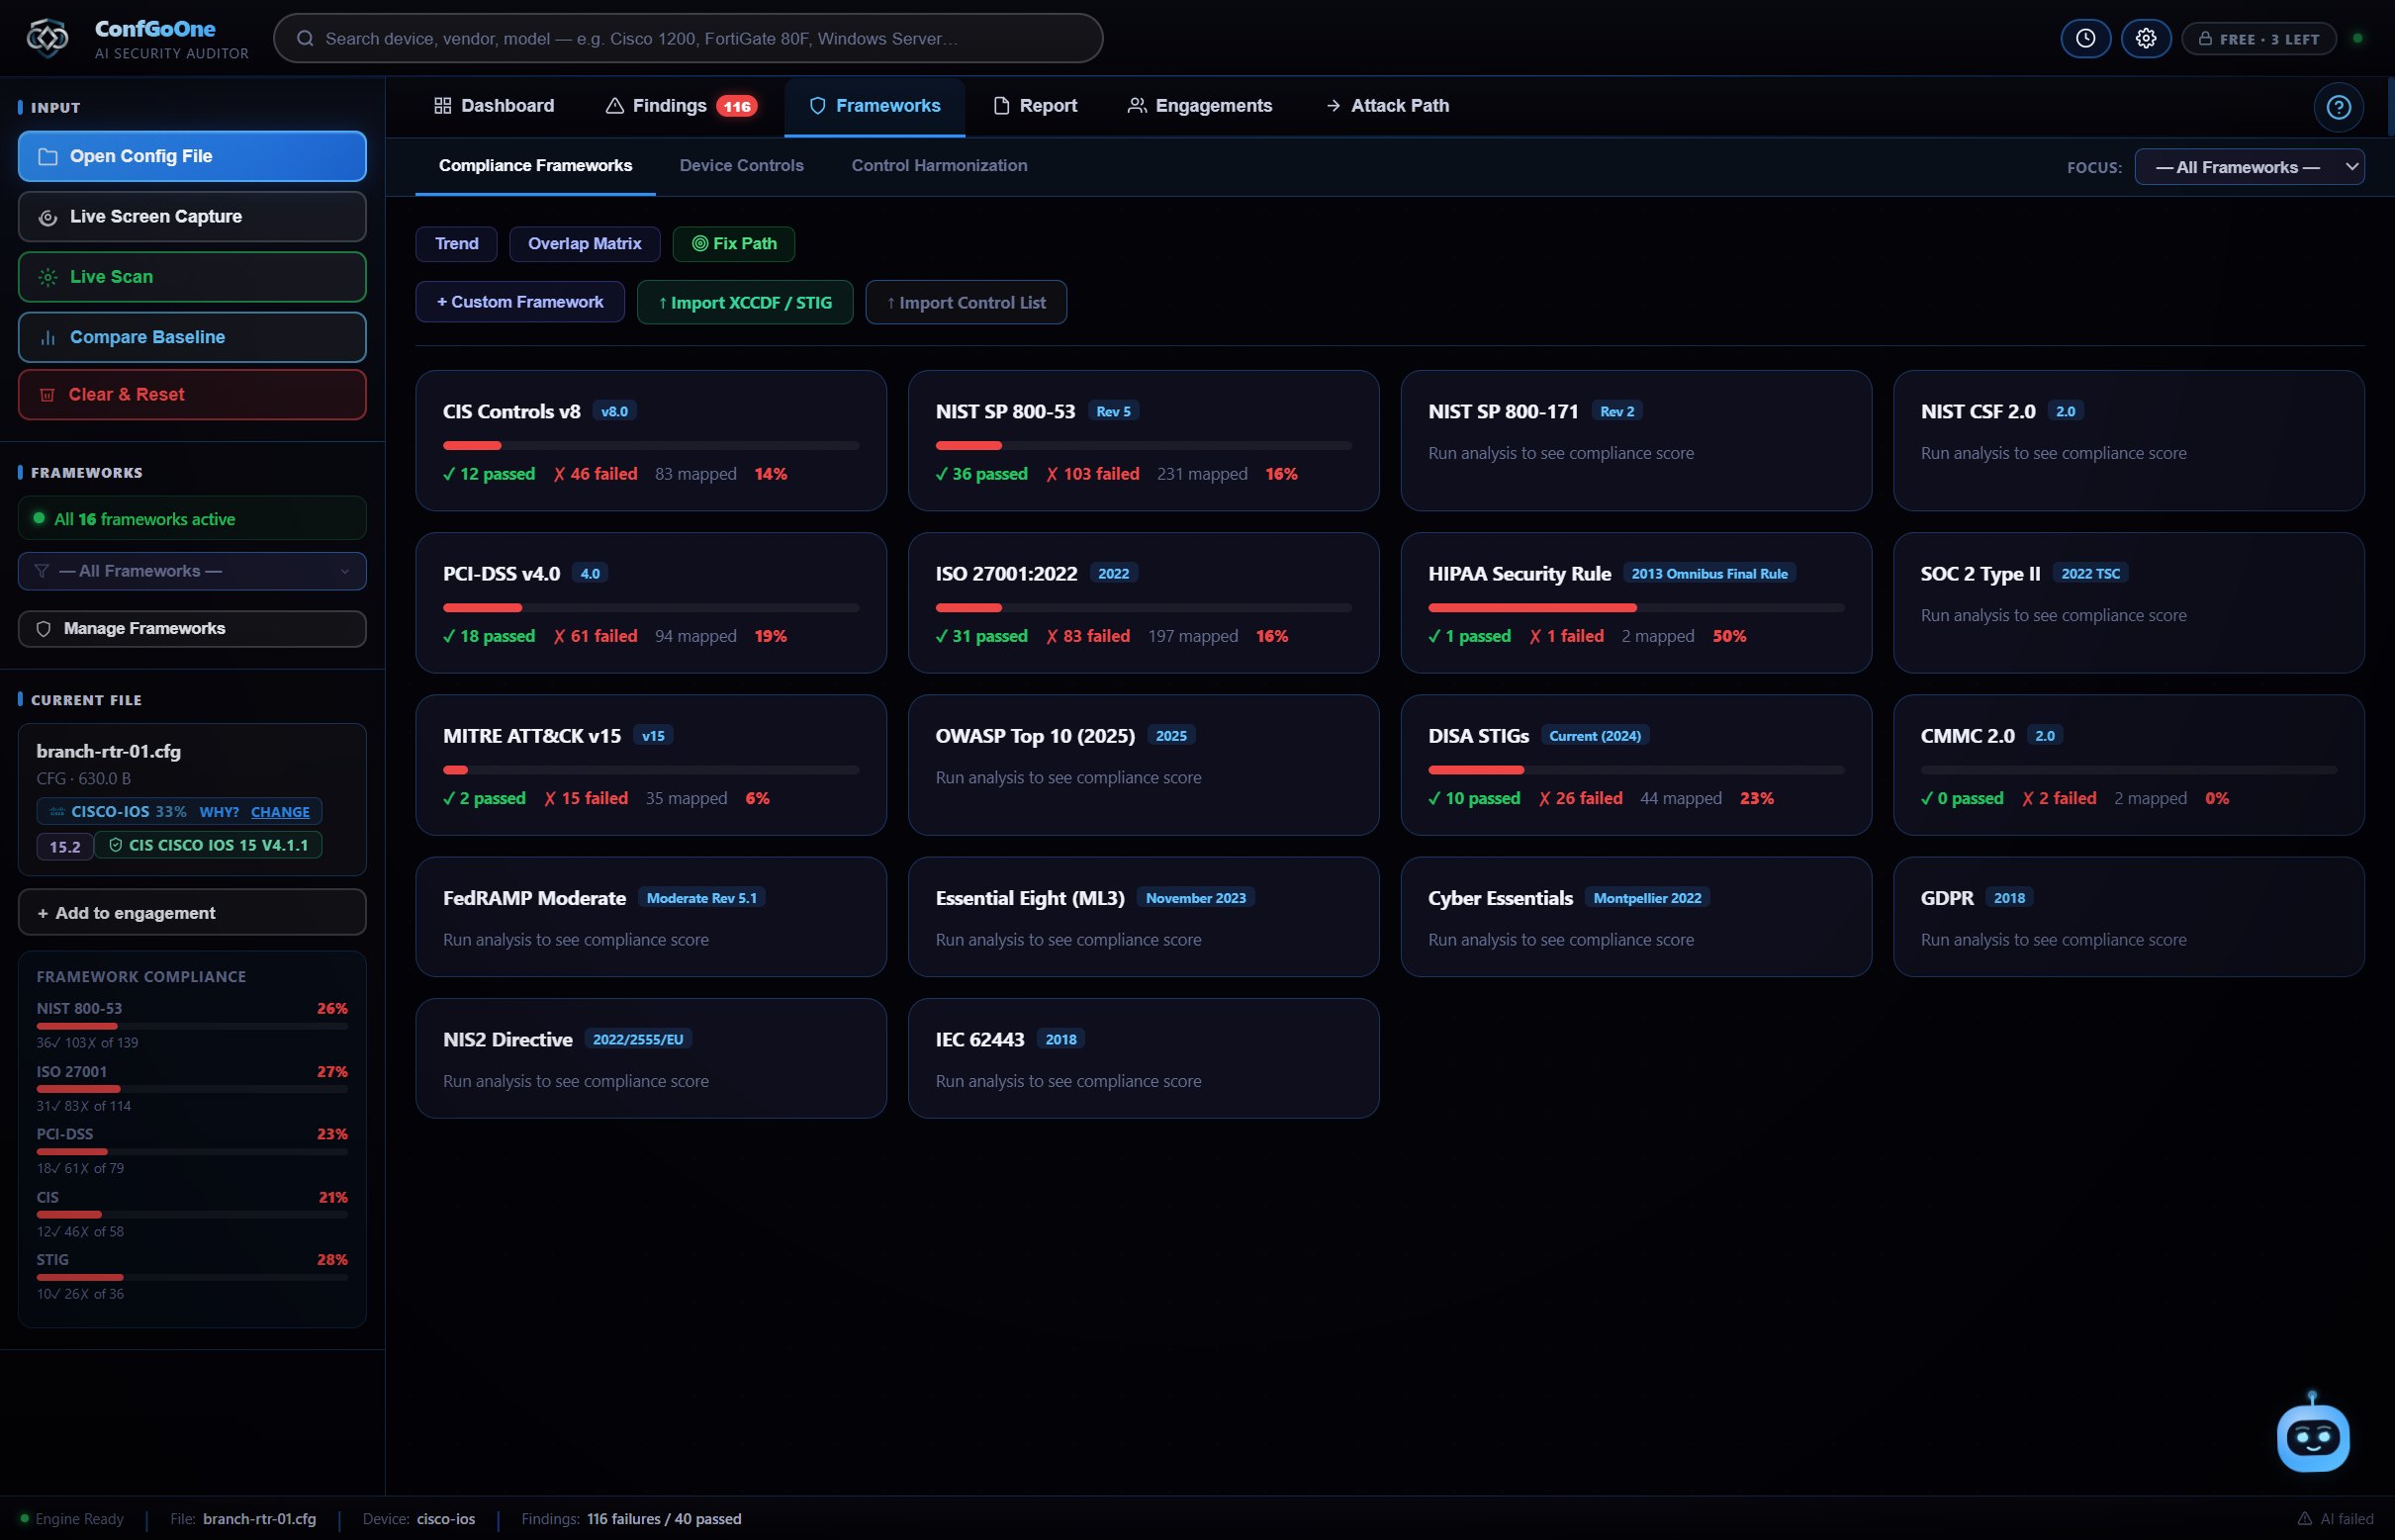
Pick CIS as your only standard and ConfGoOne audits the configuration against it — findings, scores and the report all follow that choice. Every failed control comes with the evidence and the commands to fix it.
What ConfGoOne checks
A sample of the real checks in ConfGoOne's rule packs — each one reported with the evidence from your file and the fix.
Audit to CIS only
Choose CIS and the findings, compliance score and report cover just CIS — nothing else to filter out.
One fix, many standards
See which other standards the same fix satisfies — CIS, NIST, ISO 27001 and PCI-DSS at once.
Free to start
The free plan includes three full audits with CIS and NIST 800-53 mapping and HTML reports.
How it works
No setup, no agent, no "start scan" button.
A configuration file, a live connection or a screen capture — whichever you can get.
The device type is recognised and every setting is checked the moment the file opens.
Work through the findings with their fix commands, then export HTML, PDF, Word or a STIG checklist.
Questions
How do I check a configuration against CIS Benchmarks?
Open the configuration in ConfGoOne and choose CIS under Frameworks. The audit runs immediately and shows each CIS control as passed or failed, with evidence and fix commands.
Can the report show only CIS?
Yes. When you audit against CIS only, the findings, compliance section and report cover CIS only. The HTML report can also be filtered by framework and severity.
Which systems can be checked against CIS?
Network devices and firewalls from major vendors, Linux and Windows servers, Apache, Nginx and IIS, MySQL, PostgreSQL and SQL Server, AWS, Azure, Google Cloud, Kubernetes and Docker.
Is CIS included in the free plan?
Yes — the free plan includes CIS and NIST 800-53 mapping for three full audits.
CIS® and CIS Benchmarks™ are trademarks of the Center for Internet Security, Inc. ConfGoOne is not affiliated with or endorsed by CIS.
Related
Run your first audit in the next minute.
Three free audits. No credit card, no cloud upload — your configs never leave your PC.
Download ConfGoOne →